Reports and exports
Every report and export with its options and scope, DefectDojo, Securitm and importing external reports.
Findings leave ScanSuite through several routes: downloadable reports, exports of the pages, DefectDojo and Securitm. This page lists them all, with the options of each.
Scan reports
Every finished scan has a Report button in Scan History and a Download report button on its page. Either downloads a ZIP archive with the raw scanner output and the normalised reports:
| Format in the archive | What it is |
|---|---|
| HTML | A standalone, scrollable report. AI reports carry the risk summary, reachability ordering and the call-path or reachability diagrams inline. |
| XLSX | Spreadsheets, including the infrastructure and dependency reports with their Exploit column; see Exploits in scan reports. |
| JSON | The normalised findings, for another system to read. |
| Markdown | The AI Pentest engagement write-up. |
A scan's report holds what that scan found. To report on everything a product has, use the Vulnerabilities exports below.
Exports of the pages
| Where | What you get |
|---|---|
| Scan History → Download reports | The reports of the scans you ticked, in one ZIP, each as <scan id>-report.zip. |
| Scan History → Export CSV | One row per scan the filters list: dates, type, mode, target, product, status, who started it, what it changed and what it cost. |
| Product page → Download latest reports | The newest report of every target of one product, in one ZIP with a folder per target. See The product page. |
| Products → Export CSV | One row per product: risk, open findings, coverage, secrets, last scan and LLM spend. |
| Products → Management report | A PDF report or ten PPTX slides on all products, for managers. Options below. |
| Vulnerabilities → Export | Five formats of the findings; see the next section. |
| Assets → Export | The hosts in the current view as XLSX or JSON. See Assets. |
| Credentials → Export to XLSX | The product's credentials: the ticked ones, or all; Export verified to XLSX takes only the verified ones. Vulnerability managers, operators and team admins. |
| Vuln DB → Export CSV | The CVEs the current filters show, up to 20,000 rows. See Exploitable Vulnerabilities Database. |
Vulnerabilities → Export
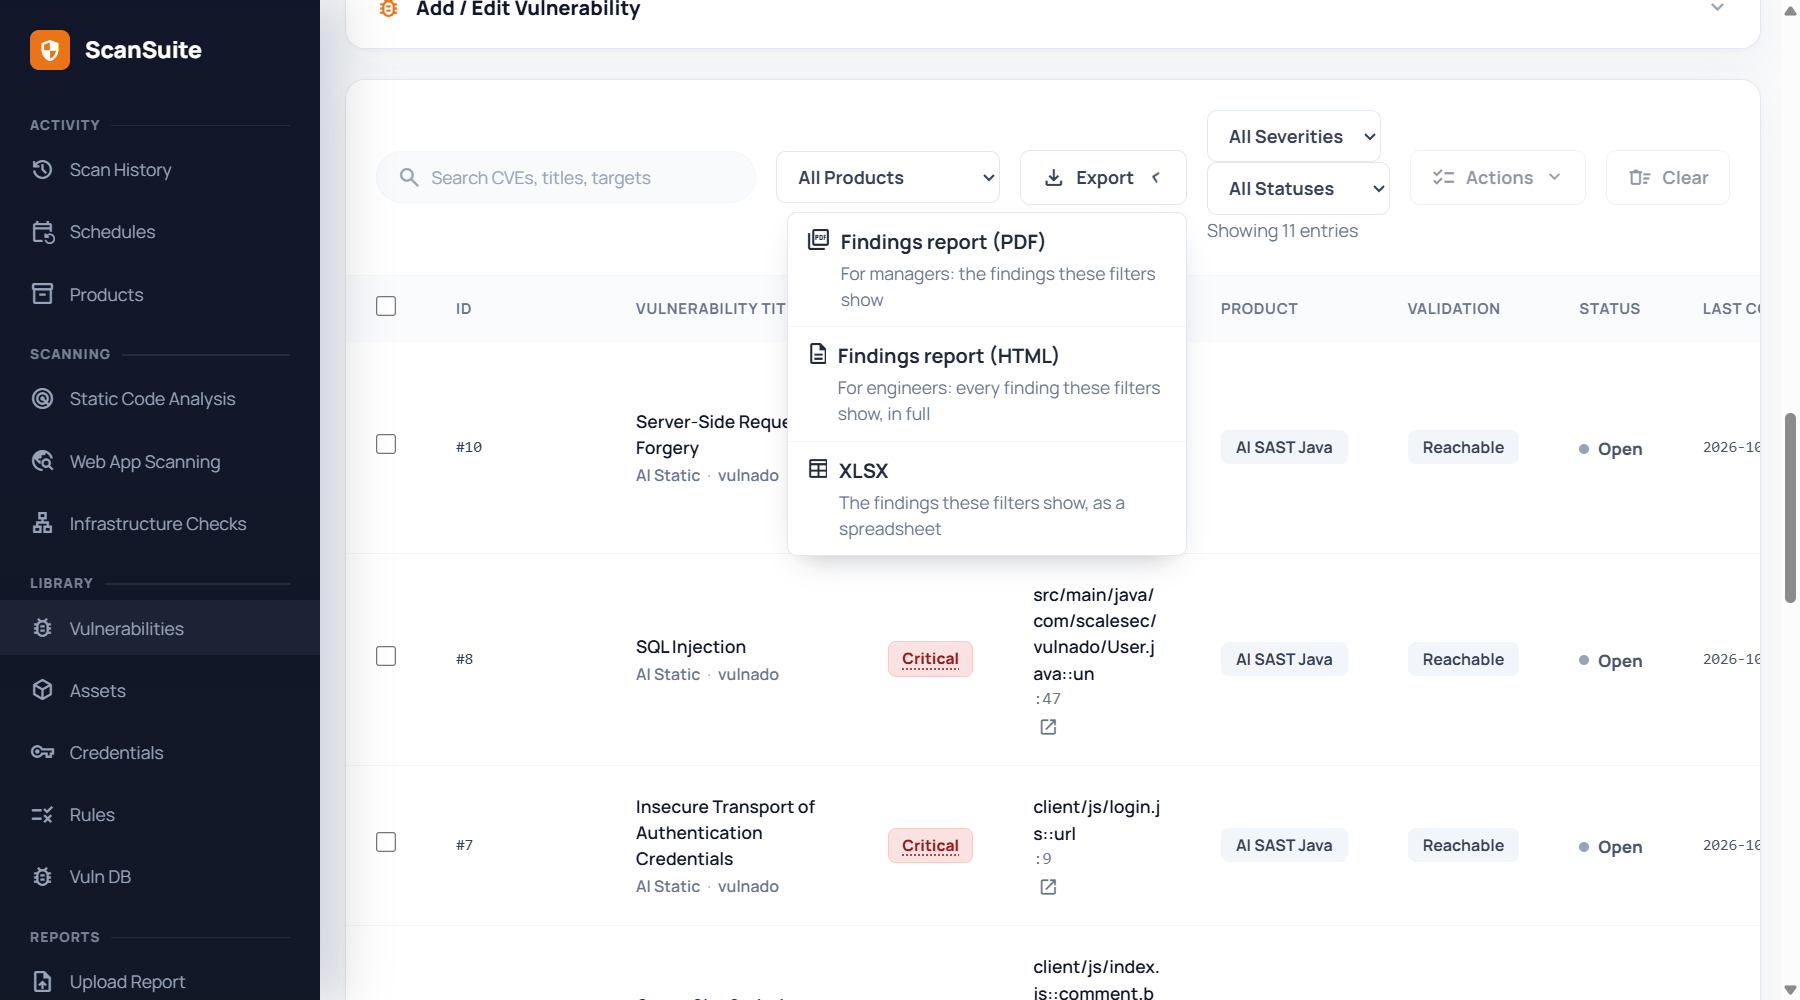
The Export menu on the Vulnerabilities page:
| Item | What it is | Which findings | With All Products |
|---|---|---|---|
| Findings report (PDF) | For managers: figures and the findings these filters show. | The page's filters: search, product, severity, status, class, scan and asset | Yes |
| Findings report (HTML) | For engineers: every finding these filters show, in full, with no row limit. Code findings carry the file, vulnerable code, mitigation and reachability; application and infrastructure findings carry the host or URL, CVE, evidence and remediation. | The page's filters | Yes |
| XLSX | The findings these filters show, as a spreadsheet, spelled as the page shows them. | The page's filters | Yes |
| JSON | Every stored row of the product, for another tool to read. | The whole product, filters ignored | No: choose a product |
| ServiceNow XLSX | Ready to upload to ServiceNow: opens new findings, closes fixed ones. See Rescans and fix verification. | The whole product, filters ignored | No: choose a product |
To export exactly what you are looking at, set the filters first, then export the PDF, HTML or XLSX.
Report options
The PDF, HTML and management reports open a dialog before downloading:
| Report | Option | What it does | Default |
|---|---|---|---|
| Findings report (PDF) | Comment on page 1 | Free text printed on the first page. Optional, up to 600 characters. | Empty |
| Findings report (PDF) | List every Critical and High finding, not only the first 40 | Appends the full list instead of the first 40. | Off |
| Findings report (HTML) | Findings to include | Code and dependencies, Applications and infrastructure, or Both, as two sections with their own columns. Each choice shows how many findings it has; an empty one is disabled. | Both |
| Findings report (HTML) | Comment under the title | Free text under the report title. Optional, up to 600 characters. | Empty |
| Management report | Format | PDF report (to read, send and keep) or Slides (PPTX): ten slides with editable charts, to present. | PDF report |
| Management report | Period | Last 7 days, Last 30 days, Last 90 days, Last quarter, This quarter to date, Last 12 months or All time. | Last 90 days |
| Management report | Comment on page 1 | Free text. Optional, up to 600 characters. | Empty |
| Management report | Append the list of open Critical and High findings | PDF only. | Off |
| Management report | Append every product’s scanned repositories | PDF only. | Off |
Click Download PDF, Download HTML or Download slides. The company name, logo, classification label and paper size of the PDF reports and slides come from the Management reports card on the team's Scanning tab (Teams page), which team admins and operators can change.
Every role can download reports and exports. Download latest reports, the Scan History CSV, and the management and findings reports are recorded in the team's activity log.
Which findings reach the Vulnerabilities page
The AI scans, Nessus and custom rules always store their findings on the Vulnerabilities page; the classic scanners do so according to the team's Store scanner findings setting. The rule and its defaults are in Vulnerability Management, under "Which findings are stored here". Findings that are not stored are still in the scan reports and in DefectDojo.
DefectDojo
DefectDojo is optional, and recommended for the classic scanners. Once it is connected, the static analysis engines each have their own Export to DefectDojo switch in their settings on the scan form, and the infrastructure and web scanners send their reports to the product's engagement. There, DefectDojo's own reporting, metrics and Jira integration apply — see Classic scanner results in DefectDojo.
Some engines never export to DefectDojo. Secrets found in code are reviewed on the Credentials page and dependency findings in the scan report. AI Native SAST, AI DAST and AI Pentest findings are tracked in ScanSuite's own vulnerability management. Hidden Paths results are held back by default because of what the data contains.
Securitm
Nessus, OpenVAS and Network Discovery reports upload to SGRC Securitm after each scan once the team's Securitm address and API key are set — see Export to Securitm.
Importing an external report
Upload Report in the sidebar opens Import report, which imports a report produced outside ScanSuite into a product's DefectDojo engagement.
| Field | What it is | Default |
|---|---|---|
| Choose a report file | The report file. | None |
| Report Type | Tenable Scan, OpenVAS Parser, Acunetix Scan, Nmap Scan, SARIF, GitLab SAST Report or Trivy Scan. | Tenable Scan |
| Product / Eng ID | The product and its engagement. Only products with a DefectDojo engagement are listed. | The last product used |
Click Upload. Importing is for operators and team admins.
Importing needs DefectDojo: without it, Upload is disabled, because there is nowhere to put the findings. Imported reports are not sent to Securitm.
Alerts
Email and Telegram alerts about new hosts and changed host ratings are described in Assets.
Last reviewed 2026-10-19